Stop your agents
from going rogue
Prismor helps enterprises control their agents' identity, access, and runtime actions

 Dashboard/Overview
 cursor4
 claude-code4cursor6
 langchain-api2cursor2Dashboard/Policiesclaude-codeMacBook ProcursorMacBook AircursorCI runner
 codexLinux desktop
 windsurfMacBook Pro
 copilotMacBook Prolangchain-apiGPU nodeclaude-codeMacBook AirDashboard/Audit log
An immune layer for every agent action
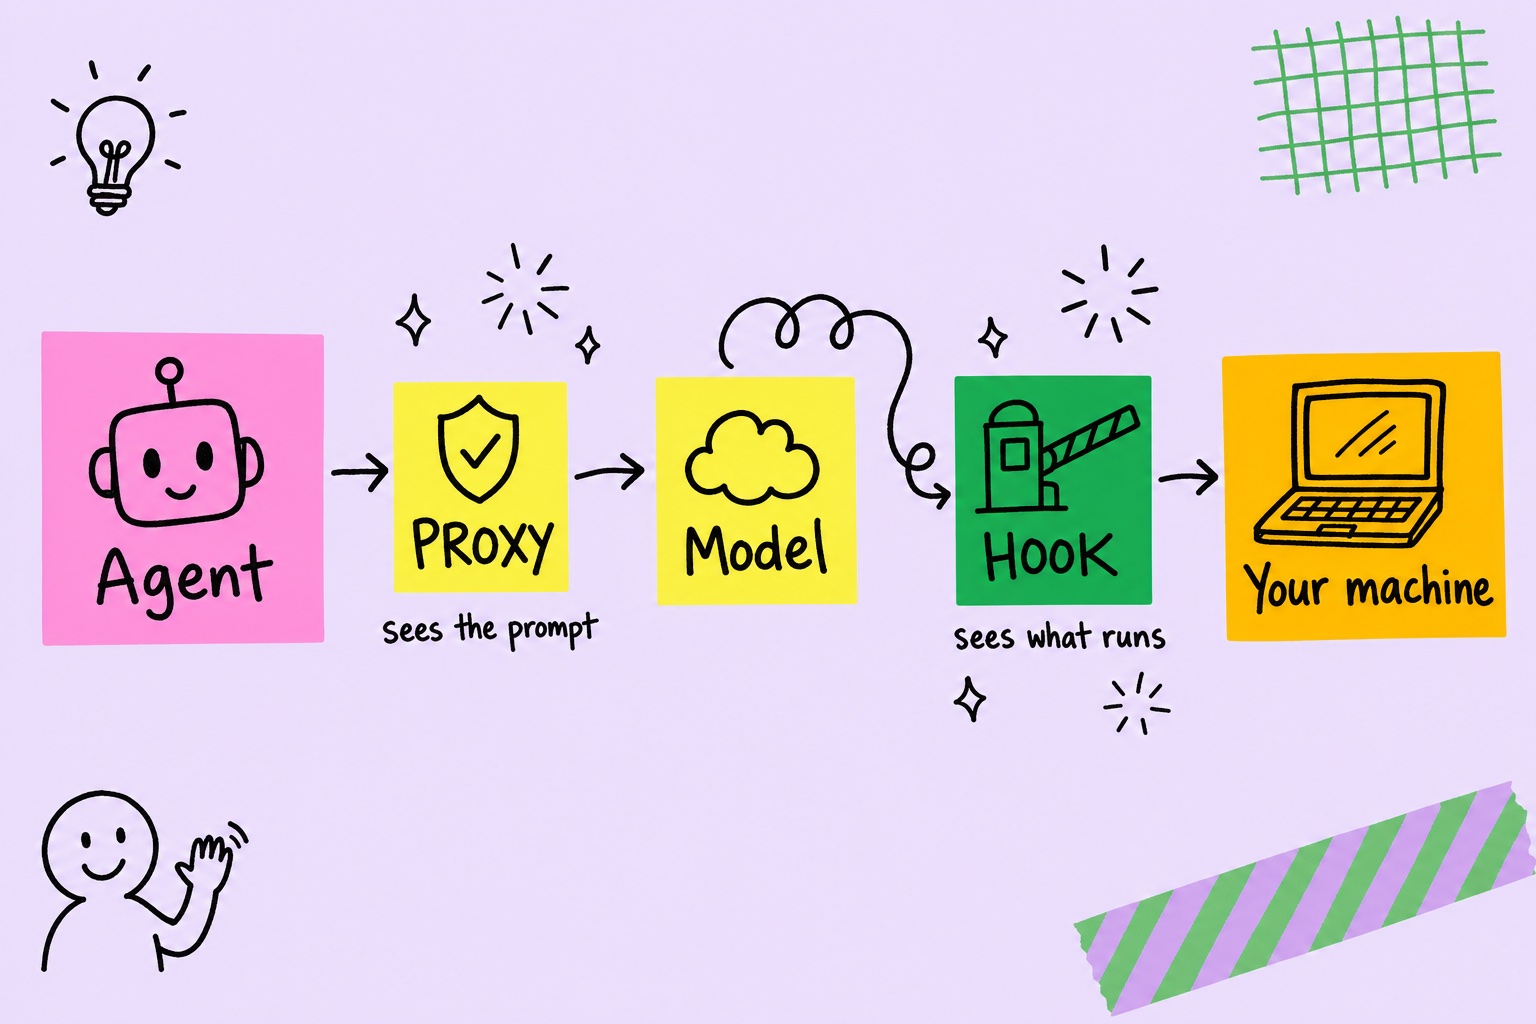
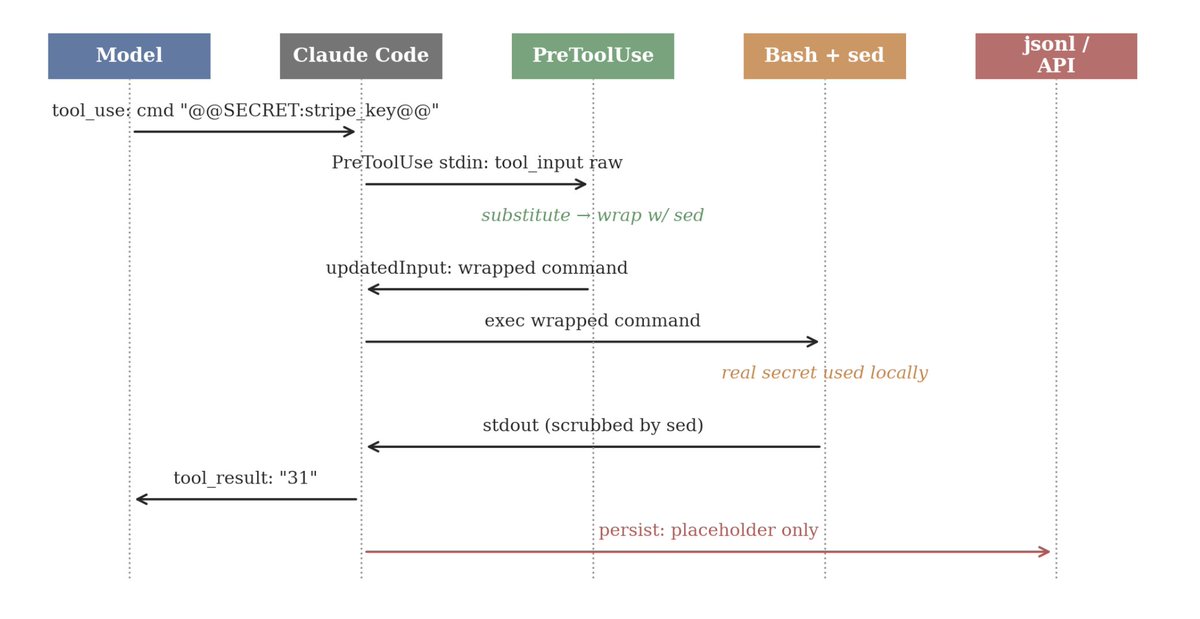
Your agents run hundreds of tool calls a session. Prismor catches each one before it executes, blocks the destructive ones, and strips secrets out before they reach the model. Every call lands in an audit trail you can read back later. Works with the OpenAI Agents SDK, MCP agents like Claude Code and Cursor, LangChain, and CrewAI
Every tool call intercepted, masked, and loggedSecurity rules your whole team can version
Write your security rules once and apply them from the CLI. Set defaults for the org, override them per team, grant exemptions per person. You pull, lint, and apply the same way you ship infra config, and every change sits in git for review
Policies versioned, linted, and applied like infraEvery agent action, on the record
Your agents run in the background. You see the output. Prismor captures what happened before it: every tool call at interception, what Prismor blocked, what it masked, who triggered the session. The full timeline is live in your dashboard while the agent is still running. Your security team can pull an export any time
Full session timeline, tool by toolOne security layer for every agent your team uses
Connect Prismor once and keep the same runtime policy, secret protection, and audit trail across coding agents, SDKs, and custom MCP workflows.


A closed loop that gets safer with every decision
Export agent activity to your observability stack, involve a human when policy needs context, then turn approvals, denials, and incident outcomes into better policy recommendations.
Send traces, policy outcomes, and audit events into the tools your security team already monitors.
 Datadog
 OpenTelemetry
 New Relic
 Splunk
 Grafana
Notify the right owner, request approval, or route an exception without stopping the entire workflow.
 Slack
Prismor uses guided decisions and recurring patterns to recommend tighter rules, reviewed before they are applied.
What developers are saying
AI agents can run commands before you get a chance to review them. This repo adds a checkpoint
Your agent is about to call a tool and you have no pause button in the session
Your guardrail can warn you and still wave the command through. Prismor's docs make the distinction explicit: observe only logs; enforce can block, but warn/log actions still allow the call
a seatbelt for claude code
Looking for a promising tool: Prismor. Tell me something is wrong in the agentic coding landscape without telling me something's wrong
open-source tooling that answers a real bill question always finds users
if you use Codex or Claude Code, you probably need this
bookmarked, thanks for sharing
Love the MCP gateway angle. One policy layer across everything is the right abstraction
bro this is actually clean, i've had claude code almost run rm -rf on my server once. policy checks would've saved me
the observe mode is the part i'd want tested: how often does it flag legitimate shell commands, and who maintains those policies when the repo changes?
Honestly, AI trading bots need this more than humans
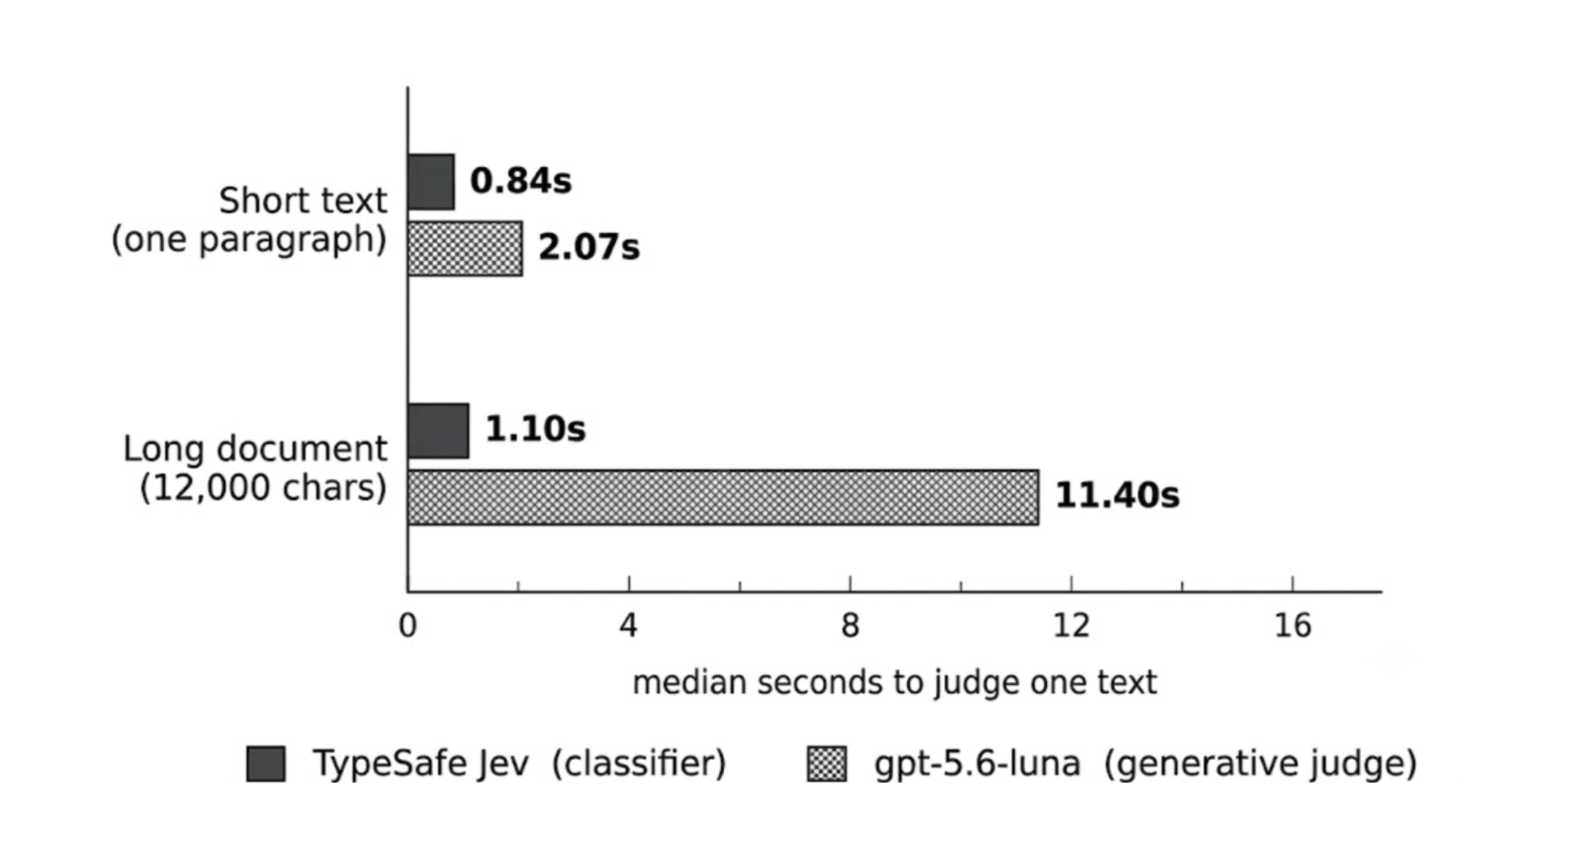
gm, open source control plane that gates every tool call sounds like the missing guardrail. how heavy is the latency?
enforce mode saves wallets tbh
the enforce vs observe switch is smart! teams can see the blast radius before
This is a real gap. The agent part gets all the attention, but visibility and control are what make it usable in production
nice take on agent iam, the guardrail scoping feels solid. how do you handle secret rotation across delegated sub agents?
Local first security for agents is a strong direction. Secret redaction is table stakes, but policy enforcement around tool calls and package installs is where this gets really interesting
this is genuinely needed. most agent stacks rn are a black box once you deploy them, and the "we'll add observability later" crowd finds out the hard way when something exfiltrates a token
Open source is the way to go! Superb demo and great product
super cool product!
Tried it for 3 of my repositories. Super awesome man!
This is awesomeee
I think this is a very solid approach
too good
Hats off for providing us with this!!
security is key especially as models become increasingly capable!
As enterprises are adapting agents into their workforce, security becomes very crucial part of the workflow. Looking forward for great work
so cool!
From agent chaos to auditable control
Connect
Wrap your agent framework with Prismor in one step. MCP, the OpenAI Agents SDK, LangChain, CrewAI. Your existing agents keep working.
Intercept
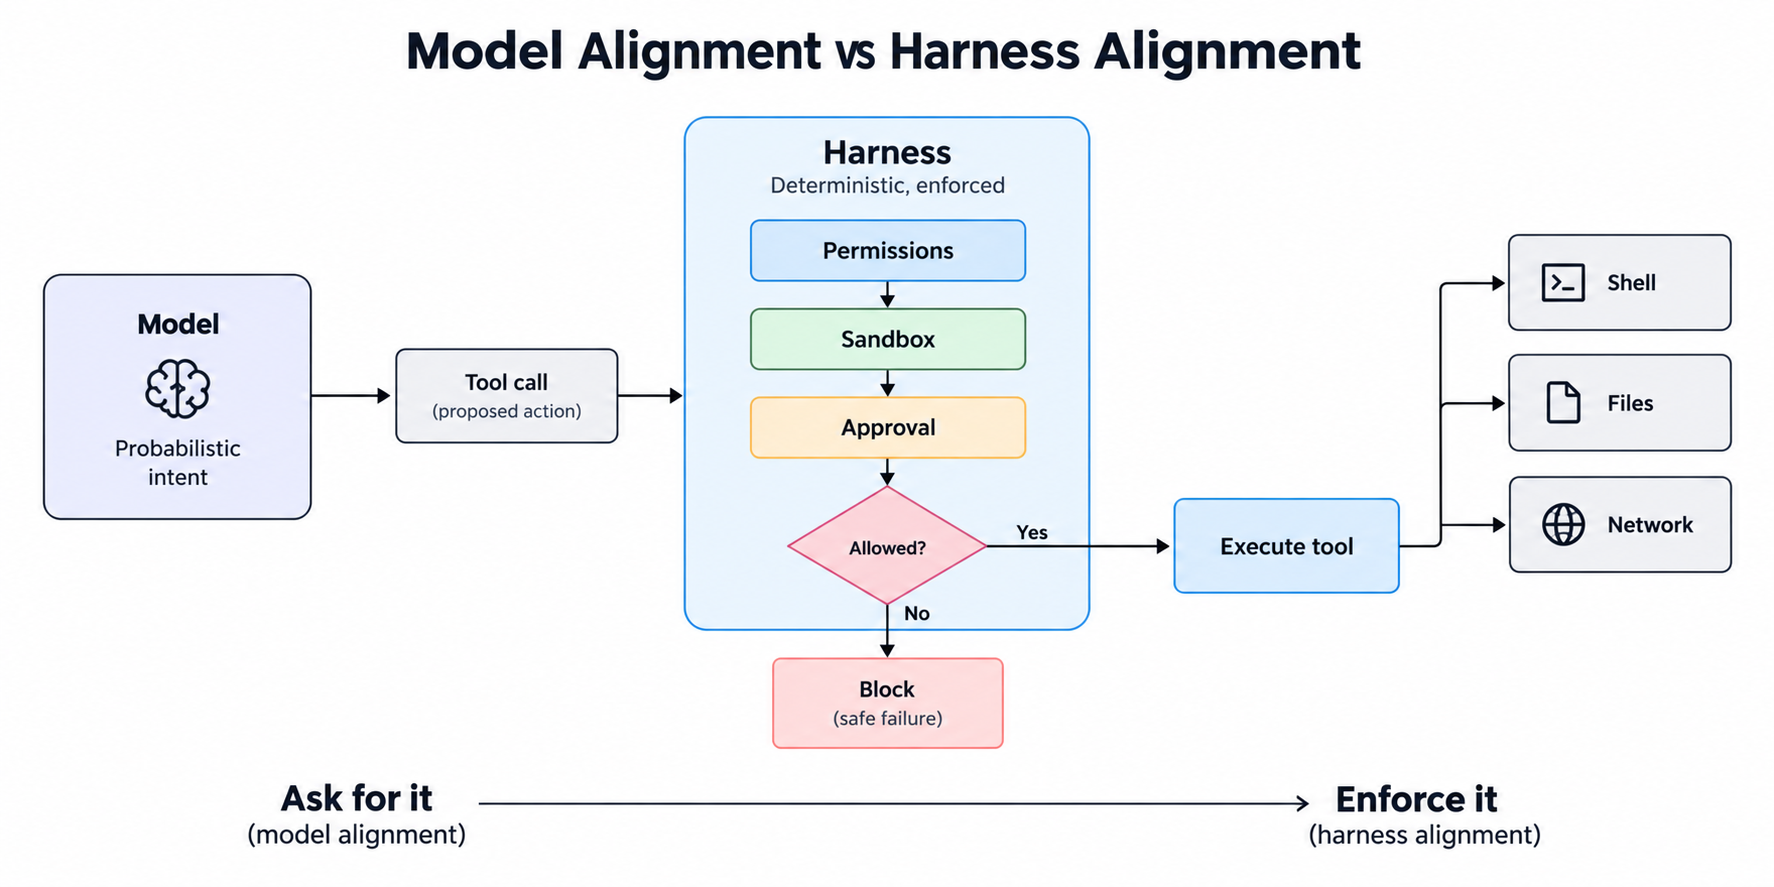
Every tool call routes through Prismor before it executes. The agent has no path around it.
Enforce
Your active policy decides each call: allow, block, or mask. Secrets never reach the model. Destructive commands never run.
Audit
Read the full timeline of every agent action in the dashboard: arguments, outcome, user, session. Export it when compliance asks.
Improve
Update policies from the CLI as your conventions change. Every rule is versioned and reviewed by a teammate, same as infra config.